2Captcha Alternatives: Which Are Actually Drop-In?
Seven 2Captcha alternatives compared on API compatibility, documented challenge types and resale terms, from each provider's own pages, read October 2026.
The right 2Captcha alternative depends on why you are leaving. If you want to change one base URL and keep your code, only a couple of services document that, and each one supports a narrower set of challenge types through that mode than through its own API. If you are prepared to touch the integration, the field opens up, and the deciding factors become documented challenge coverage, what happens to your money on a failed solve, and whether the provider's terms let you build what you are building. We run CaptchaNo, so we have already said where we differ from 2Captcha; this post is about the whole field.
Every claim below comes from the provider's own documentation or terms, read on 22 October 2026. We quote no prices, because rates in this category change without notice, and we make no speed or accuracy claims about anyone, because we cannot run another company's account under controlled conditions.
Why the usual "2Captcha alternatives" pages are useless
The directory pages that rank for this query do not list captcha solvers. G2 files 2Captcha under e-commerce fraud protection, so its alternatives page recommends Signifyd, Sift and SEON, which detect fraud rather than solve challenges. AlternativeTo's list includes a Web3 app built around maths puzzles. Capterra's alternatives page returned a 404 when we checked. The vendor listicles are better, but most rank the publisher's own product first, quote figures without a source, and never answer the question a developer actually has: will my existing 2Captcha integration work against this service?
That question has a precise answer, and it is the main thing this page adds.
How we compared the 2Captcha alternatives
We applied the same five checks to every service, using only its public documentation and terms. Disclosure: CaptchaNo is one of the services, and we say plainly where it does not fit.
- API contract. Does it accept 2Captcha's classic
in.php/res.phprequests, or theclientKey+taskJSON shape that 2Captcha's API v2 also uses, or something of its own? - Documented coverage of the two types that separate providers in practice: Cloudflare Turnstile and DataDome.
- Billing on failure. Whether the docs say you pay only for correct solves, and how long you have to dispute one.
- Resale and embedding terms. Whether the terms allow building a product on top.
- Free tier or trial, since "2captcha free alternative" is one of the searches that leads here.
If you want a ranked list rather than a decision tool, we keep one in our comparison of captcha solving services, built on the same sources.
2Captcha alternatives at a glance
Observed on each provider's own pages, 22 October 2026. "2Captcha v1 mode" means the service documents accepting requests written for 2captcha.com/in.php and res.php. "JSON task API" means its native API uses the same clientKey / task / websiteURL / websiteKey family as 2Captcha's API v2, which makes a port mechanical even though task type names differ.
| Service | 2Captcha v1 mode | Native API shape | Turnstile | DataDome | Resale in terms |
|---|---|---|---|---|---|
| DeathByCaptcha | Yes, documented (token, text, image and coordinate tasks only) | Own HTTP API | Documented, marked beta | Documented, marked beta | Not addressed (selling your account is prohibited) |
| CapMonster Cloud | Only through a Windows interceptor app | JSON task API | Documented | Documented, own proxy required | Prohibited (clause 5.3) |
| CaptchaAI | Claimed on its homepage | 2Captcha-style | Documented | Not listed | Not checked |
| Anti-Captcha | Not documented | JSON task API | Documented | Not in its task list | Not checked |
| CapSolver | Not documented | JSON task API | Documented | Documented, own proxy required | Prohibited |
| SolveCaptcha | Not stated on its own site | 2Captcha-style (res.php) | Documented | Documented | Not checked |
| NopeCHA | No | Own Token API | Documented | Not listed | Not addressed |
| CaptchaNo | No | Own REST API, one shape for every type | Documented | Documented, own proxy required | Permitted, documented programme |
"Not checked" means we could not read that provider's full terms for this post. "Not addressed" means we read them and found no clause either way.
Which 2Captcha alternatives are actually drop-in?
Two services say you can keep your 2Captcha client and change where it points. One of them documents exactly how, and the limits.
DeathByCaptcha: documented emulation, four task families
DeathByCaptcha publishes a 2Captcha-compatible endpoint pair: api.deathbycaptcha.com/2captcha/in.php for uploads and /2captcha/res.php for results, balance and reports. Your 2Captcha key becomes username:password. The page is explicit that only text, image-group, coordinate and token captchas work through this mode, and that any other method returns ERROR_URL_METHOD_FORBIDDEN. For software that hard-codes 2captcha.com, it suggests a hosts-file redirect, which is a workable hack for a desktop tool and a bad idea on a server.
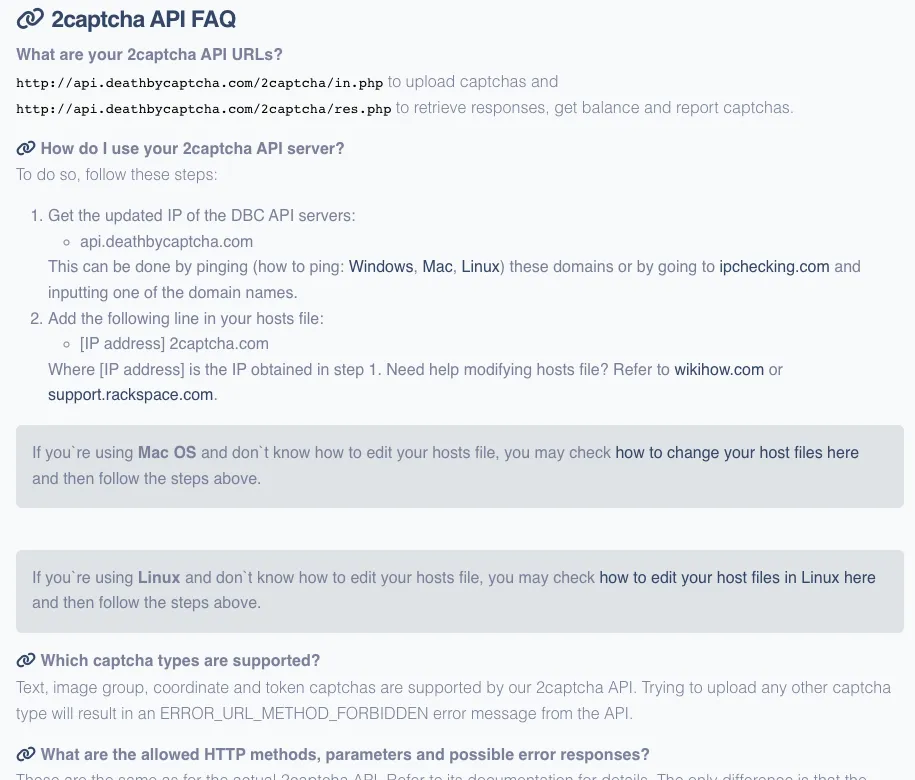
DeathByCaptcha's 2Captcha API page, 22 October 2026: the emulated URLs, the username:password key format, and the four supported task families.
Elsewhere in its documentation, DeathByCaptcha also emulates the Antigate and DeCaptcher protocols, bills per correctly solved captcha, and refunds a solve you report as wrong within an hour of upload.
CaptchaAI: a claim on the homepage
CaptchaAI's homepage says that if your software has a 2Captcha option you can select it and use a CaptchaAI key, and it refers to this as an emulator. It does not publish the equivalent endpoint list on that page, so treat the claim as something to test rather than a specification. Its billing is also structurally different: monthly thread subscriptions with unlimited solves inside the thread limit, and ERROR_NO_SLOT_AVAILABLE beyond it. A migration post by its founder lists five things that do not carry over even in emulation mode, including v3 score parameters, error-string differences and proxy restrictions. That list is worth reading, because the same gaps apply to every "drop-in" claim in this market.
CapMonster Cloud: interception, not an endpoint
CapMonster Cloud's documentation states that it supports the Anti-Captcha v1 and v2, RuCaptcha, RipCaptcha, 2Captcha, BypassCaptcha and DeathByCaptcha APIs. Read the page that says so, though: the mechanism is a Windows program called CapMonsterInterceptor that intercepts captcha traffic bound for those services on the machine it runs on and redirects it. "Other platforms support are in development," as of 22 October 2026. For a Windows desktop bot that is convenient; for a Linux scraper or a container, there is no 2Captcha-compatible HTTP endpoint to point at, and you port to its native JSON API instead.
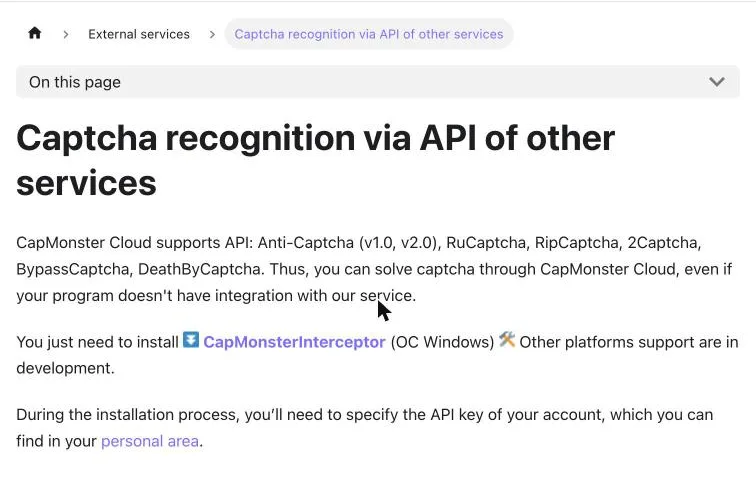
CapMonster Cloud's "API of other services" page: compatibility is delivered by a Windows interceptor, not by an HTTP endpoint.
SolveCaptcha: compatibility asserted by others
Several third-party articles describe SolveCaptcha as fully API-compatible with 2Captcha. Its own homepage uses the same res.php naming and the same ERROR_NO_SLOT_AVAILABLE convention, but we did not find the compatibility claim stated on the site itself, and the site names no legal entity. We list it as "not stated on its own site" rather than repeat someone else's description.
The JSON task API family: a port, not a rewrite
2Captcha's own API v2 is built on JSON: POST api.2captcha.com/createTask with clientKey and a task object, then getTaskResult until status is ready. Its v1 documentation says the classic in.php/res.php API "continues to be stable and supported", so nobody is forced to move. But if you are on v2, or willing to adopt it, Anti-Captcha, CapSolver and CapMonster Cloud all use the same request family. The endpoints are api.anti-captcha.com/createTask, api.capsolver.com/createTask and api.capmonster.cloud/createTask, each taking clientKey, a task with a type, and an optional callback URL.
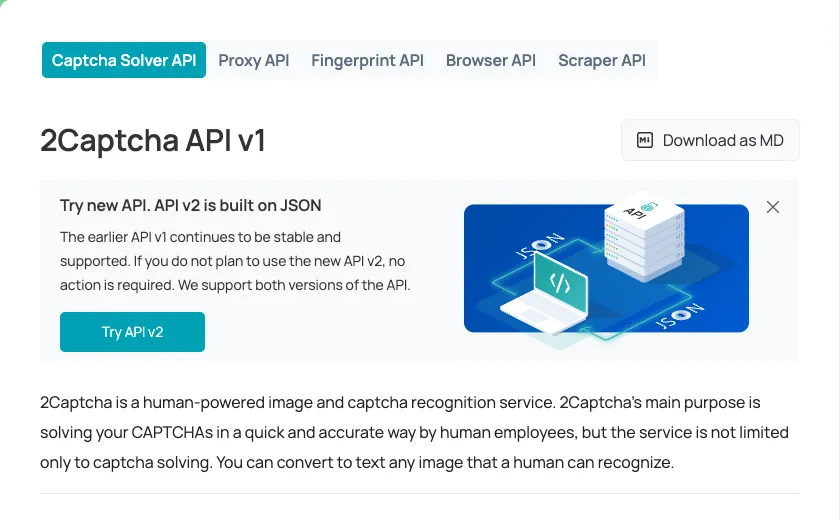
2Captcha's API v1 page, 22 October 2026: v1 stays supported, v2 is the JSON task API that other providers share.
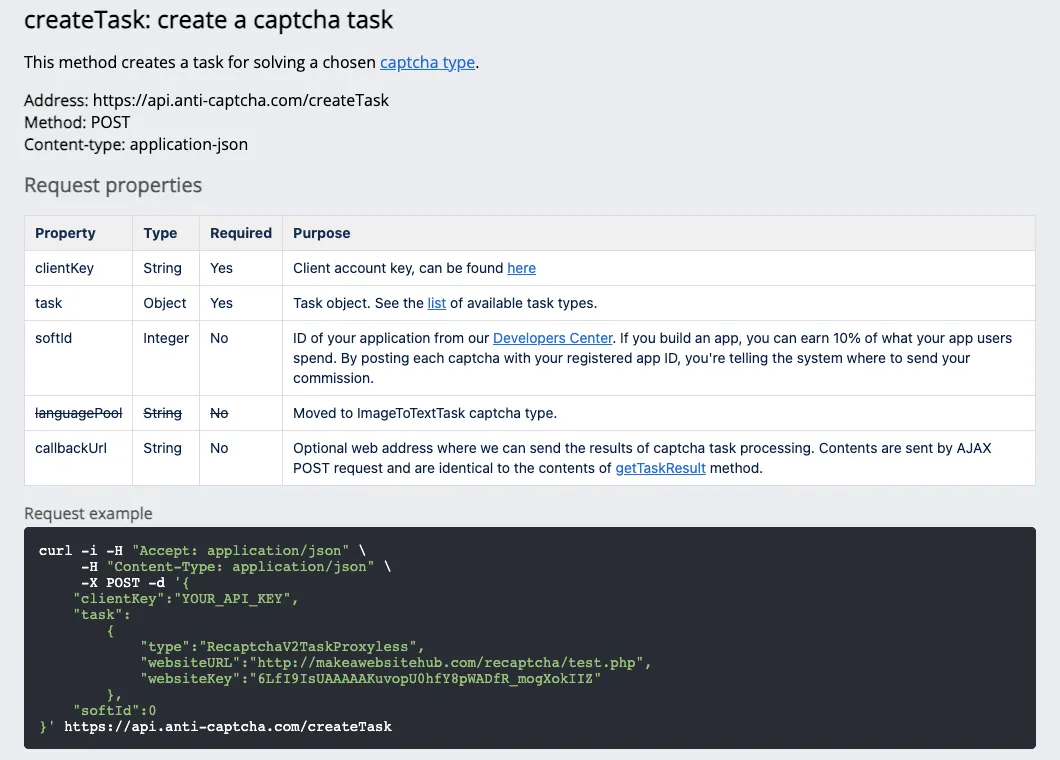
Anti-Captcha's createTask reference: the same clientKey and task shape, with its own task type names.
What differs inside that family is the vocabulary and the extras. Task type names are not interchangeable (2Captcha's RecaptchaV2TaskProxyless exists at Anti-Captcha too, but CapMonster's DataDome task is CustomTask with a class field, and CapSolver's is DatadomeSliderTask). CapSolver adds an optional appId and returns some image tasks synchronously. Proxy fields are structured differently from provider to provider. Expect a day of work per provider to map types and error codes, not a URL change.
What does not carry over when you switch from 2Captcha
Whichever route you take, these are the things that break quietly. Check each one before the first production request.
- Task type names and required fields. Even inside the JSON family, every provider has its own catalogue. Build a mapping table and fail loudly on anything unmapped.
- Error codes. Some providers reuse 2Captcha's strings; others return numeric
errorIdvalues with their own descriptions. Any retry logic keyed on an exact string needs re-checking. - Proxy semantics. On DataDome, CapSolver and CapMonster Cloud both require your own proxy, and CapSolver restricts the user agent to specific strings it lists. A token-type integration that never sent a proxy will need to.
- reCAPTCHA v3 parameters. Action and minimum-score fields are named and honoured differently. Re-read the target page's action name rather than carrying over whatever your 2Captcha call sent.
- Affiliate and software IDs.
soft_idandsoftIdare provider-specific. Drop them or re-register. - Polling cadence. 2Captcha asks for at least five seconds between result checks; others publish different guidance or none. Over-polling gets rate-limited.
- The billing model. Per-solve balances, thread subscriptions with daily or concurrency caps, and credit bundles are not comparable without normalising to cost per accepted completion, and some change your capacity-planning maths entirely.
- Refund windows. DeathByCaptcha gives you an hour to report a bad solve; SolveCaptcha says fifteen minutes; CapSolver's terms say it offers no refunds in any form. Your error handling has to raise disputes inside the window or not bother.
- Session matching. A token minted behind one IP and user agent and submitted from another gets rejected no matter who minted it. If your acceptance rate drops after a switch, check this before blaming the provider; our guide to why valid captcha tokens get rejected gives the diagnostic order.
Pick a 2Captcha alternative by the reason you are leaving
There is no single best alternative, only the one that removes your particular constraint. These are the constraints we see most often.
You want to change one line and move on
DeathByCaptcha is the only service that documents the emulated endpoints and their limits. If your traffic is reCAPTCHA tokens or image captchas, it will work; if it is Turnstile or DataDome, those are marked beta there and are not part of the emulation mode anyway. CaptchaAI's claim is worth a test if a thread subscription suits your volume profile.
You need DataDome or another session-graded system
DataDome returns a cookie bound to the exit IP that earned it, not a reusable token, which is why providers that support it insist on your proxy. CapSolver, CapMonster Cloud, SolveCaptcha, DeathByCaptcha (beta) and CaptchaNo document it; Anti-Captcha, NopeCHA and CaptchaAI do not list it. Before choosing, read what DataDome actually checks, because a surprising share of "DataDome problems" are block pages a solver cannot help with. Our DataDome solver page sets out the request we need.
You build a product that other people use
Read the terms before the docs. CapSolver's terms list "any form of reselling CapSolver services" under prohibited activities. CapMonster Cloud's user agreement, effective 1 August 2025, says in clause 5.3 that "reselling the Service to third parties is prohibited" and in clause 5.2 that unused funds are non-refundable. DeathByCaptcha's and NopeCHA's terms do not address resale, which is better than a prohibition but still not a licence (DeathByCaptcha does prohibit selling your account, and NopeCHA states that all services are non-refundable). Anti-Captcha's terms page did not render for us, so read it yourself before you build. We built our reseller programme because this gap exists; the full reasoning is in our CapSolver comparison.
You want a free alternative to 2Captcha
There are three honest answers, none of which replaces a paid API at volume. Buster is a GPL-3.0 browser extension for Chrome, Edge and Firefox that solves the reCAPTCHA audio challenge with speech recognition; it is for a person at a keyboard, not a script. NopeCHA's site describes a free plan of up to 100 recognitions every 24 hours, intended for hobby projects, with token solving for reCAPTCHA v2 and v3, hCaptcha and Turnstile and higher daily caps on paid plans; its developer FAQ says free credits are withheld from VPN and proxy IPs. Most pay-per-solve providers, including us, give a small trial balance so you can measure before you deposit. "Free" at scraping volumes does not exist; what you can get free is an evaluation.
You run AI agents rather than scripts
CapMonster Cloud publishes an MCP server in its docs, and CaptchaNo has a self-hosted MCP example. The property that matters for agents is a typed, deterministic result the model can branch on, with the cost of the call in the response, so a runaway loop is visible before it empties a balance.
How CaptchaNo compares as a 2Captcha alternative
We are not a drop-in replacement, and we would rather say so than let you find out. Our API is one request shape for every type we support: POST /v1/solve?wait=60 with a bearer key, a type, the page URL and the sitekey, and the response carries the token, the user agent it was minted with, the cost and the solve time. Without wait you poll a task endpoint every five seconds. Failed solves cost nothing, credit is prepaid, and resale is explicitly permitted. The full reference is at our captcha solver API page.
What we support: reCAPTCHA v2 (checkbox, invisible, callback), classic reCAPTCHA v3, reCAPTCHA Enterprise checkbox-style widgets, Cloudflare Turnstile, DataDome with your proxy, and image captchas. What we do not support: hCaptcha, score-based reCAPTCHA Enterprise keys, Arkose, GeeTest and the regional types. If a meaningful share of your 2Captcha traffic is on that second list, we are the wrong alternative, and 2Captcha's catalogue, which is the longest we have seen published, may be the right place to stay. The difference between Enterprise widgets we can solve and the score-based keys we cannot is explained in our reCAPTCHA Enterprise explainer.
What we will not tell you is that we are faster than 2Captcha or anyone else. Every solve we return shows its real duration in your dashboard, and we publish nothing about other companies' timings.
How to test an alternative before moving traffic
Run a split, not a demo. Send a slice of real production challenges, with the same proxy and user agent you submit with, to the candidate for a day, and record cost per accepted completion rather than per returned token. Trigger a deliberate failure (an unreachable proxy, a wrong sitekey) and check whether you were charged. Re-run at your peak hour, because queue depth is what changes between providers over a day. And confirm that the automation you are running is something the target permits and the provider's terms allow; ours are set out in our acceptable use policy, and no alternative changes what a target site's terms say.
Frequently Asked Questions
What is the best alternative to 2Captcha?
There is no single best alternative, because people leave 2Captcha for different reasons. If you need a documented compatible endpoint, DeathByCaptcha is the only one that publishes it, with limits. If you need DataDome, choose from the providers that document it and require your proxy. If you resell or embed solving, eliminate the providers whose terms prohibit it first. Shortlist on your constraint, then run a split test on your own traffic.
Is there a free alternative to 2Captcha?
Only for small or manual use. Buster is an open-source browser extension that solves reCAPTCHA audio challenges for a person at a keyboard. NopeCHA describes a free plan of up to 100 recognitions every 24 hours for hobby projects, with higher daily caps on paid plans, and it withholds free credits from VPN or proxy addresses. Pay-per-solve providers, CaptchaNo included, offer trial balances to evaluate. Nothing free holds up at scraping volume.
Which captcha solvers are compatible with the 2Captcha API?
DeathByCaptcha documents emulated 2captcha in.php and res.php endpoints for token, text, image and coordinate tasks. CaptchaAI claims on its homepage that software with a 2Captcha option works with its key. CapMonster Cloud redirects 2Captcha-bound traffic through a Windows interceptor program rather than an HTTP endpoint. Anti-Captcha, CapSolver and CapMonster share 2Captcha's JSON task-API shape, which makes porting mechanical but not automatic.
Can I switch from 2Captcha without rewriting my code?
Sometimes, within limits. Through DeathByCaptcha's emulation you change the base URL and the key format, but only four task families are accepted and other methods return an error. Even then, error strings, v3 score parameters, proxy handling, polling cadence and billing semantics differ, so a one-line change usually becomes a day of verification. Budget for mapping task types and re-testing session matching on your real targets.
Does switching providers fix tokens that keep getting rejected?
Usually not, because most rejections are session mismatches rather than bad tokens. If the token is minted behind one IP address and user agent and submitted from another, the target refuses it regardless of which service produced it. Pass the proxy and user agent you will submit with on the solve request, and measure accepted completions rather than returned tokens, before concluding that the provider is at fault.
Measure the alternative on your own traffic
The only comparison that counts is a split test on the challenges you actually hit. Start with a free trial balance, point it at a slice of your production traffic, and compare cost per accepted completion against what you pay today.